AI Governance for Small Business: Two Simple Controls
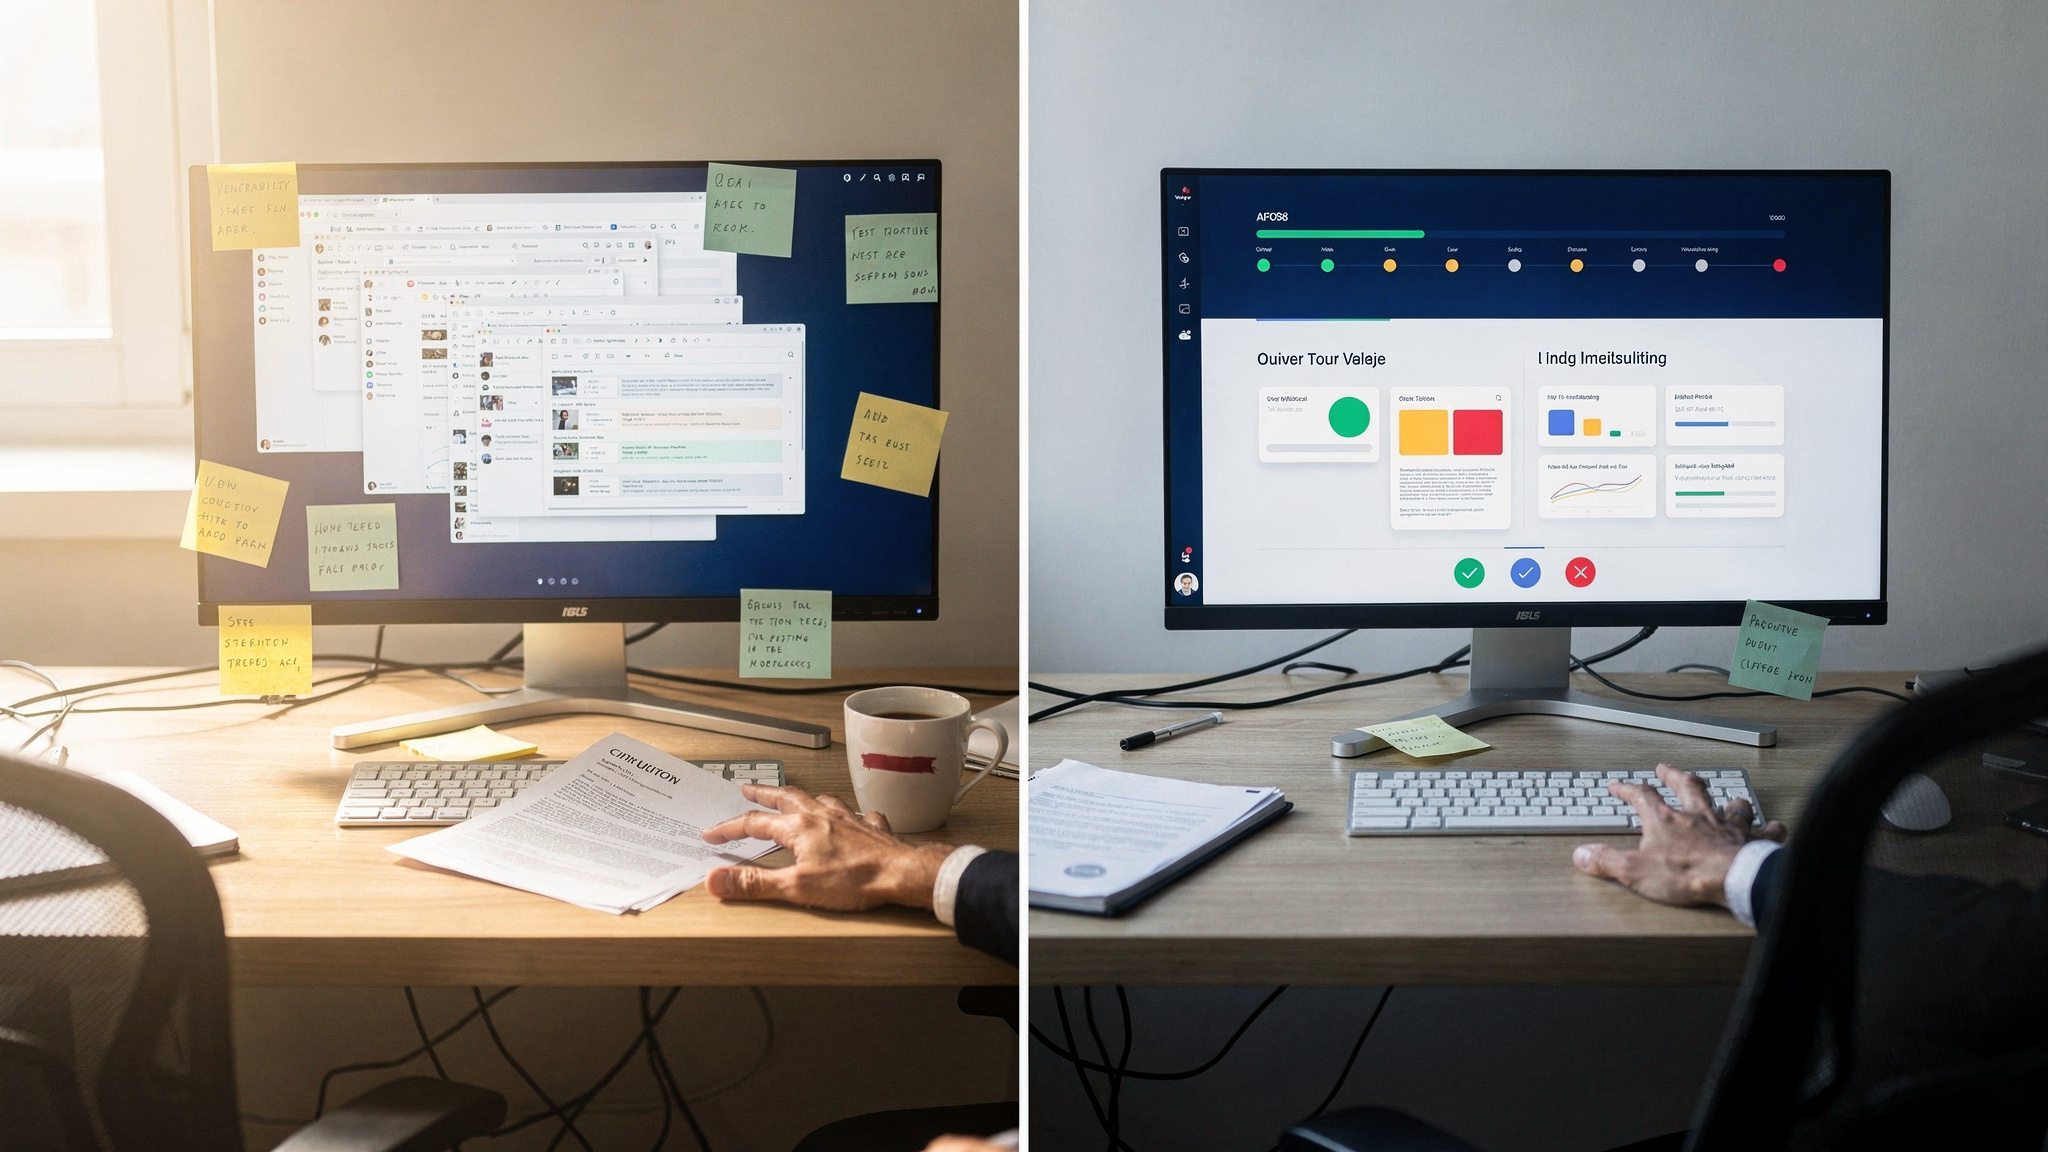
- You cannot make an AI model trustworthy, but you can build controls to make your business accountable.
- Limit data exposure by defining a strict never-list of confidential categories that AI tools can never access.
- Create a simple logging process to document prompts, inputs, outputs, human sign-offs, and source verification.
- Enforce human checkpoints on any AI output that could materially affect a person or business relationship.
- Secure written vendor agreements covering data handling, model training, auditability, and liability before signing contracts.
Here is what a failure of AI governance for small business actually looks like. Someone on your team pastes a client's financials into a free chatbot to speed up a summary. The summary is good. But you can no longer say where that data went, who can see it, or whether it just helped train a model you don't own.
A few weeks later, an AI-drafted email to a customer cites a service guarantee your business doesn't offer. It goes out under your name. The customer believes it and makes a decision based on it. Now you either honor a promise you never made or explain why your own email was wrong.
Six months after that, a client disputes a rate that was set with AI help and asks how it was calculated. Nobody can reconstruct what the tool was given, what it produced, or who signed off. The decision may have been perfectly sound. You just can't show it.
None of these arrived with an error message. Nothing announced that "the AI broke." Each one showed up as paperwork, and none of them is a model-quality problem. Swap in a better model and every outcome stays the same. The first is a failure of access: the tool reached data it never should have seen. The second and third are failures of record: nothing captured who checked what before it counted.
There's a harder truth underneath. A model can be helping and you can still own the result. When AI output becomes a decision in pricing, contracts, hiring, or client communication, the consequence attaches to your business, not the software. The tool drafted the words. Your name published them.
Most owners respond to this by trying to work out whether the AI is trustworthy. They read reviews, compare benchmarks, and ask vendors for assurances. It feels responsible. It's also a question with no answer you can act on, because nobody can promise you a model will behave, including the company that built it. This guide replaces it with two questions you can answer: what can your AI reach, and what can you prove it did?
The Two Controls That Make AI Governance for Small Business Work
Every control worth implementing falls into one of two categories. It's either an access control or an evidence control.
Access answers a simple question: what can this system reach, and therefore what's the worst thing that can happen? It sets the blast radius before anything goes wrong. If a tool can only read your scheduling calendar, your worst day is a calendar problem. If it can read your inbox, your client files, and your accounting system, your worst day is much worse. That was decided the moment you connected it.
Evidence answers a different question: can I reconstruct what happened and show it to someone? It decides whether an incident is explainable or existential. The same mistake reads very differently when you can produce the reviewer, the source, and the reasoning. "We're not sure what happened" is a much worse position.
This isn't a beginner's simplification. It's the structure underneath the frameworks large organizations use. The U.S. General Services Administration's AI compliance plan requires high-impact AI to come with impact statements, independent evaluation, human review, privacy assessments, and a listing in a public inventory of AI use cases. Sort those and they fall into two piles. The inventory and privacy assessments define what can be reached. The impact statements, evaluation, and review produce the record. Enterprise governance is these two controls with more paperwork attached.
The practical payoff is that compliance becomes finite. "Is our AI safe?" has no end and no answer. "What can it reach?" and "What can we prove?" have concrete answers you can write down this week. Once those answers are on paper, you've done more governance than most businesses your size.
If this instinct sounds familiar, it's the same one behind our guide to reliable AI automation: stop trying to make the model behave, and change the shape of the system around it. Reliability and governance are the same move aimed at different risks.
Control One: Limit What the AI Can Reach
The single most effective safeguard is also the simplest. Give AI only the data the task requires. Not the full database, not the whole inbox, not the entire client record. A tool that can only see two fields can only leak two fields.
Make minimum necessary access an operating habit. Classify your data roughly into public, internal, and confidential. Limit what can reach each class. Then expose only the fields needed to finish the job. An AI that drafts job-status updates for a contractor's customers needs a first name, a job date, and a status. It doesn't need payment history, notes from the last dispute, or anything else in the file.
A tool that can only see two fields can only leak two fields.
Next, write the never-list. This is the short set of data categories that may never go into any AI tool, approved or not. Confidential client data goes at the top. Depending on your business, the list might add account numbers, employee records, credentials, or anything covered by an NDA. Keep it short enough to remember. This one rule shuts down most exposure before it starts.
That rule also changes how you think about shadow AI, meaning staff using tools you never approved. It's almost never malicious. It's an access-control failure. A bookkeeper wants a cleaner summary, so they reach for whatever tool is already open in a browser tab. People do that when the approved path is unclear or slower. A lecture won't fix it. A short, current, genuinely usable approved-tools list will, especially if the approved tool is at least as convenient as the one they'd grab otherwise.
Then make it concrete per workflow. For each AI workflow, write three lines: which systems feed it, which fields it may use, and which it may never see. That turns an abstract policy into something usable at a desk. It's also the fastest way to spot a workflow with far more access than its job needs.
Hold vendors to a security baseline: role-based access, encryption, and monitoring for unexpected behavior. These are standard. They shouldn't be upgrades you have to ask for.
Account hygiene and AI-written phishing
Beneath all of it sits account hygiene. Use a unique password for every AI tool and turn on two-factor authentication for every AI account. It's unglamorous, and it's the difference between a scoped tool and an open door. Most breaches come from simple mistakes rather than sophisticated attacks. A carefully scoped tool behind a reused password is still an open door, just with a nicer sign on it.
Attackers use AI too. AI-written phishing has removed the tells owners were trained to spot. There's no broken grammar, no strange formatting, and the context is plausible. A message can read exactly like a client or your own boss.
You won't reliably catch these by eye, and you don't need to. Verification is a process, not a detection skill, and we walk through that process in how to defend against deepfakes and impersonation fraud. The point here is simpler. Those scams only pay off when a single message is enough to move money or open a file. Before that's a fraud problem, it's an access problem.
Control Two: Make Sure You Can Prove What Happened
When something goes wrong, saying you were careful won't protect you. Documentation will: records showing you set controls, reviewed output, and held your vendor to its terms. The record is the protection.
Logging sounds like bureaucracy. It doesn't have to be. For anything externally visible, meaning anything a client, vendor, or the public will see, record five things. Record the prompt or workflow used, the inputs and outputs, who reviewed it, whether sources were verified, and where it went. For most small teams, a shared spreadsheet with one row per item handles this. It takes about two minutes.
Record the reasoning too, not just the result. Why a result was accepted or rejected is what lets you tune prompts, access, and escalation thresholds later. Without that, you're guessing at why a workflow started drifting.
The workflow that produces this record has four steps. Draft with AI. Check the sources. Get a human sign-off. Then publish or send. None of this slows a competent team down in any meaningful way. It turns a vague "we use AI carefully" into something you can show a regulator, a client, or an insurer.
Keep watching after launch. A workflow that was low-risk on day one can change as your data or volume changes. The tool that summarized ten intake forms a week may now handle two hundred, including fields nobody planned for. Review the log on a regular schedule and treat what you find as input, not blame. If people get punished for surfacing problems, they stop surfacing them.
Where the Human Checkpoint Actually Goes
The instinct after reading this far is to require human review on everything. Resist it. Universal review is the most common overcorrection, and it fails in a predictable way. When a reviewer sees forty AI outputs a day and thirty-nine are fine, they learn to click approve.
Use one test instead. Could a wrong answer materially affect a person or a business relationship? If yes, a human approves before anything is sent or acted on. If no, spot-checks and a clear escalation path are enough.
Some categories stay human by default. These include legal language, financial terms and pricing commitments, and hiring and employment decisions. They also include anything that affects someone's eligibility or access to a service, and any client-facing draft where trust is on the line.
The customer-facing side has its own rule: if a customer is talking to AI, say so. Most people are entirely comfortable with AI support. They're not comfortable being misled about it. "This is our virtual assistant" builds trust. Passing AI off as a person destroys trust, and the damage is out of proportion to the deception.
Regulation is moving the same way. The transparency rules in Europe's AI Act, in force since August 2026, require that people be told when they're interacting with an AI system. They also put labeling duties for deepfakes on the businesses that use them, not only on the companies that build the tools.
Be honest about how checkpoints fail. Under time pressure they degrade into ceremony. A rubber-stamped approval is worse than no checkpoint, because it creates false assurance that someone looked. We cover how to keep review real in stopping ceremonial AI oversight.
Finally, define escalation and override before you need them. Staff should know where to report an output that seems wrong, who reviews it, and what happens next. People must be able to challenge or correct an AI output, and that decision gets logged. The human is in charge, and the record proves it.
A rubber-stamped approval is worse than no checkpoint, because it creates false assurance that someone looked.
Push the Risk Into the Contract
Asking whether a product "has AI" is the wrong question when you evaluate a vendor. Nearly all of them claim to. The right question is whether the vendor helps you meet your own oversight obligations. Get the following in writing before you sign.
- Data handling: what's collected, where it's stored, how long it's retained, and who it's shared with.
- Training: whether your data is used to train their models. A vague answer here is a red flag.
- Human oversight: whether output can be reviewed, edited, approved, or blocked before it reaches a customer. A tool that sends without a checkpoint removes the control that matters most.
- Auditability: traceability for prompts, outputs, and changes, with logs you can actually access rather than logs buried inside the vendor.
- Drift: how they test and update the system, and how they'll tell you when its behavior changes.
- Liability and ownership: who owns the generated output and who carries liability if it causes harm. These are the clauses people skip and later regret.
Controls reduce the odds of a loss. Contracts and AI-specific insurance decide who pays when one slips through anyway. You want both.
The One-Page Policy You Can Write Today
None of this requires a committee or a compliance department. A minimal policy your team actually follows beats an elaborate framework nobody reads. It fits on one page:
- Approved tools, and the specific tasks each one is cleared for.
- The never-list: data categories that never go into any AI tool.
- The review standard: which outputs require human sign-off before they go out.
- The incident plan: who's notified, who acts, and how fast. Write it before you need it.
- A named owner.
The fifth item matters most. Accountability has a name on it. If "everyone" owns AI risk, no one does. In a small business the owner is usually you or one trusted operator, and that's fine. What matters is that the name is written down.
Train your team on the page and get their acknowledgment. Training is what actually reduces shadow AI, because people reach for the sanctioned tool once they know what it is and why it matters.
If you haven't started with AI yet, apply the same principle to time. Start with one tool, one clearly scoped task, and no sensitive data. Watch how it performs, then expand deliberately. Begin with the smallest possible blast radius, and widen it only once you can see what's happening.
Notice what this page doesn't do. It doesn't try to make the model trustworthy. It makes your business accountable, and that's the only one of the two you can actually deliver.
Know What Your AI Can Reach and What You Can Prove
Bring your current or planned AI workflows to a Webspenser AI governance review. You'll leave with a mapped access boundary for each workflow, your never-list, and human checkpoints placed by risk. You'll also get a logging format your team will actually maintain and the vendor terms worth renegotiating. By the end, you'll know exactly what your AI can reach and exactly what you could prove.
See Exactly Where Your AI Governance Stands
Answer a few questions and get a scored report showing your access controls, oversight gaps, and where to act first — no sales call required.
More from the blog
Keep reading and learning
Every other Tuesday, The Human Factor takes one psychological principle, drops it into a real moment in a small business, and shows what an automation does about it. Three minutes to read. No tutorials, no jargon, no AI hype. Just the reason your intake form never gets finished or your best customer goes quiet after a price change, and a fix you could have running in a day.
The moment — A real scene from a small business: who's in it, what they're trying to do, and what they do instead
Why it goes wrong — The psychology behind it in plain terms, explained through the moment rather than the textbook. One principle per issue
What the automation does — The fix, laid out as a simple flow, and what actually changed in hours or dollars